BLOG
Notes from the field
Threat analysis, detection engineering and hands-on training notes from the practice.
-
Threat digest: 2026-09-23
CISA added four exploited vulnerabilities to its Known Exploited Vulnerabilities catalog in a single day, led by a CVSS 10.0 Arista VeloCloud Orchestrator flaw with fixes still missing…
-
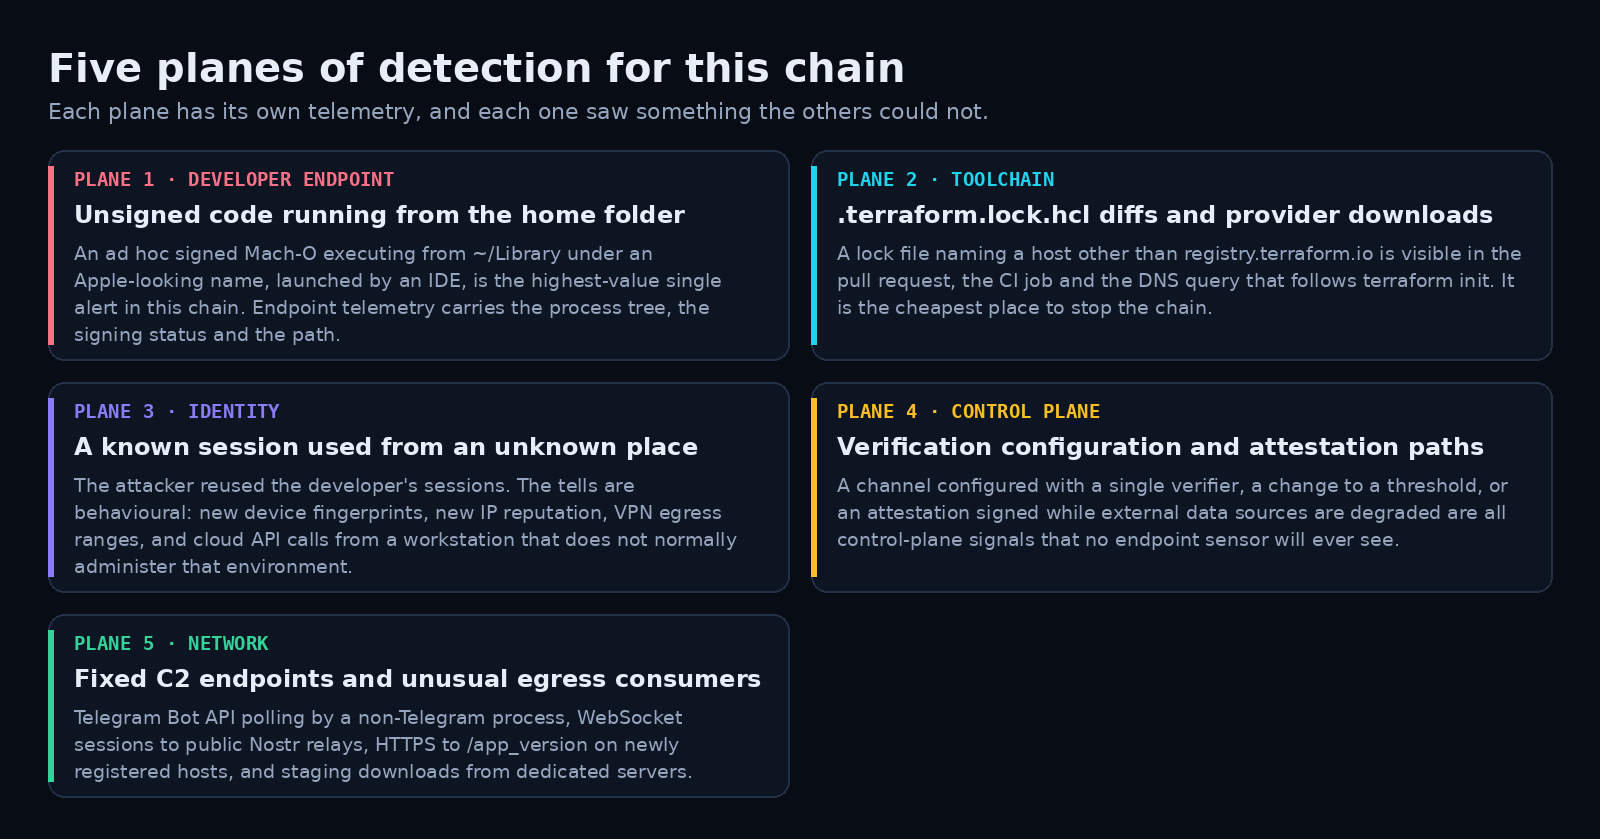
Detecting and stopping the DPRK developer chain: a control map for Terraform, macOS and cloud
The companion post to this one walks the TraderTraitor chain from a fake interview to a $292 million theft. This post is the working half: what to detect…
-
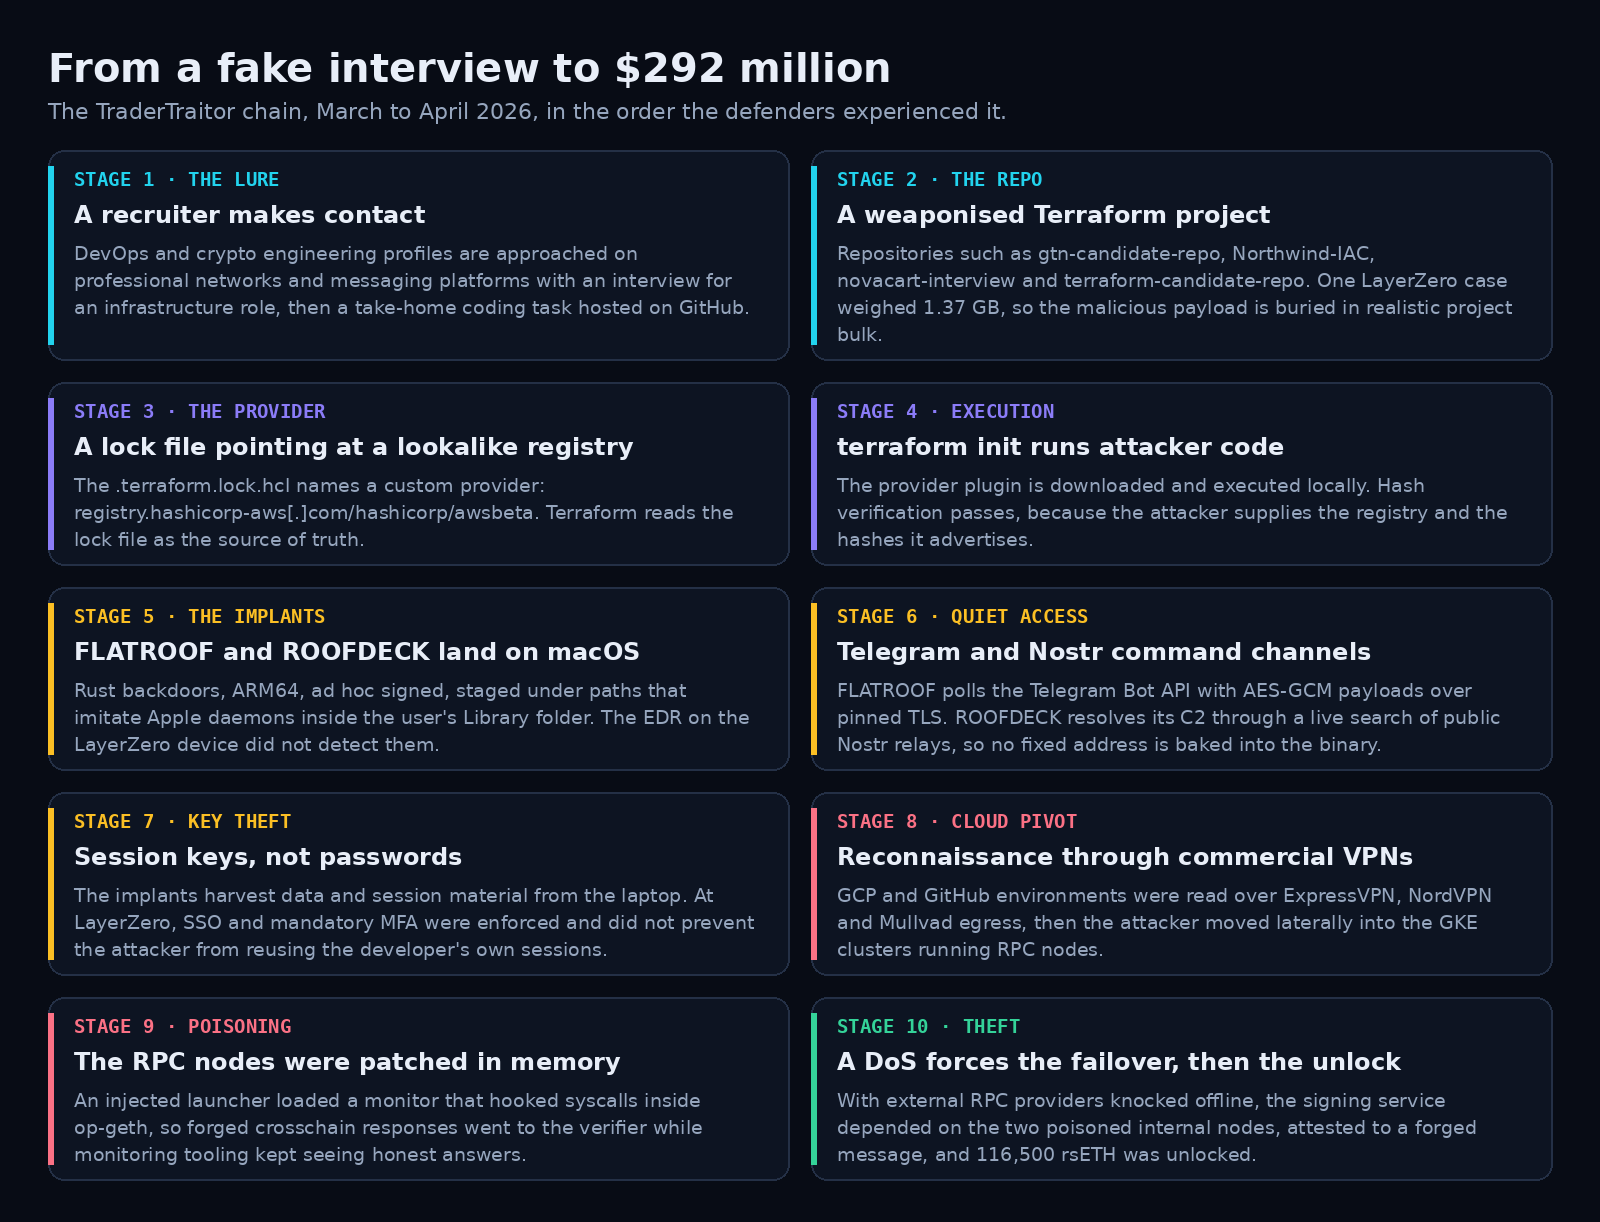
Fake interviews, a Terraform lock file and $292 million: inside TraderTraitor’s developer-first playbook
In April 2026, an attacker stole roughly $292 million in about an hour from a crosschain bridge, after spending six weeks inside the infrastructure of the protocol that…
-
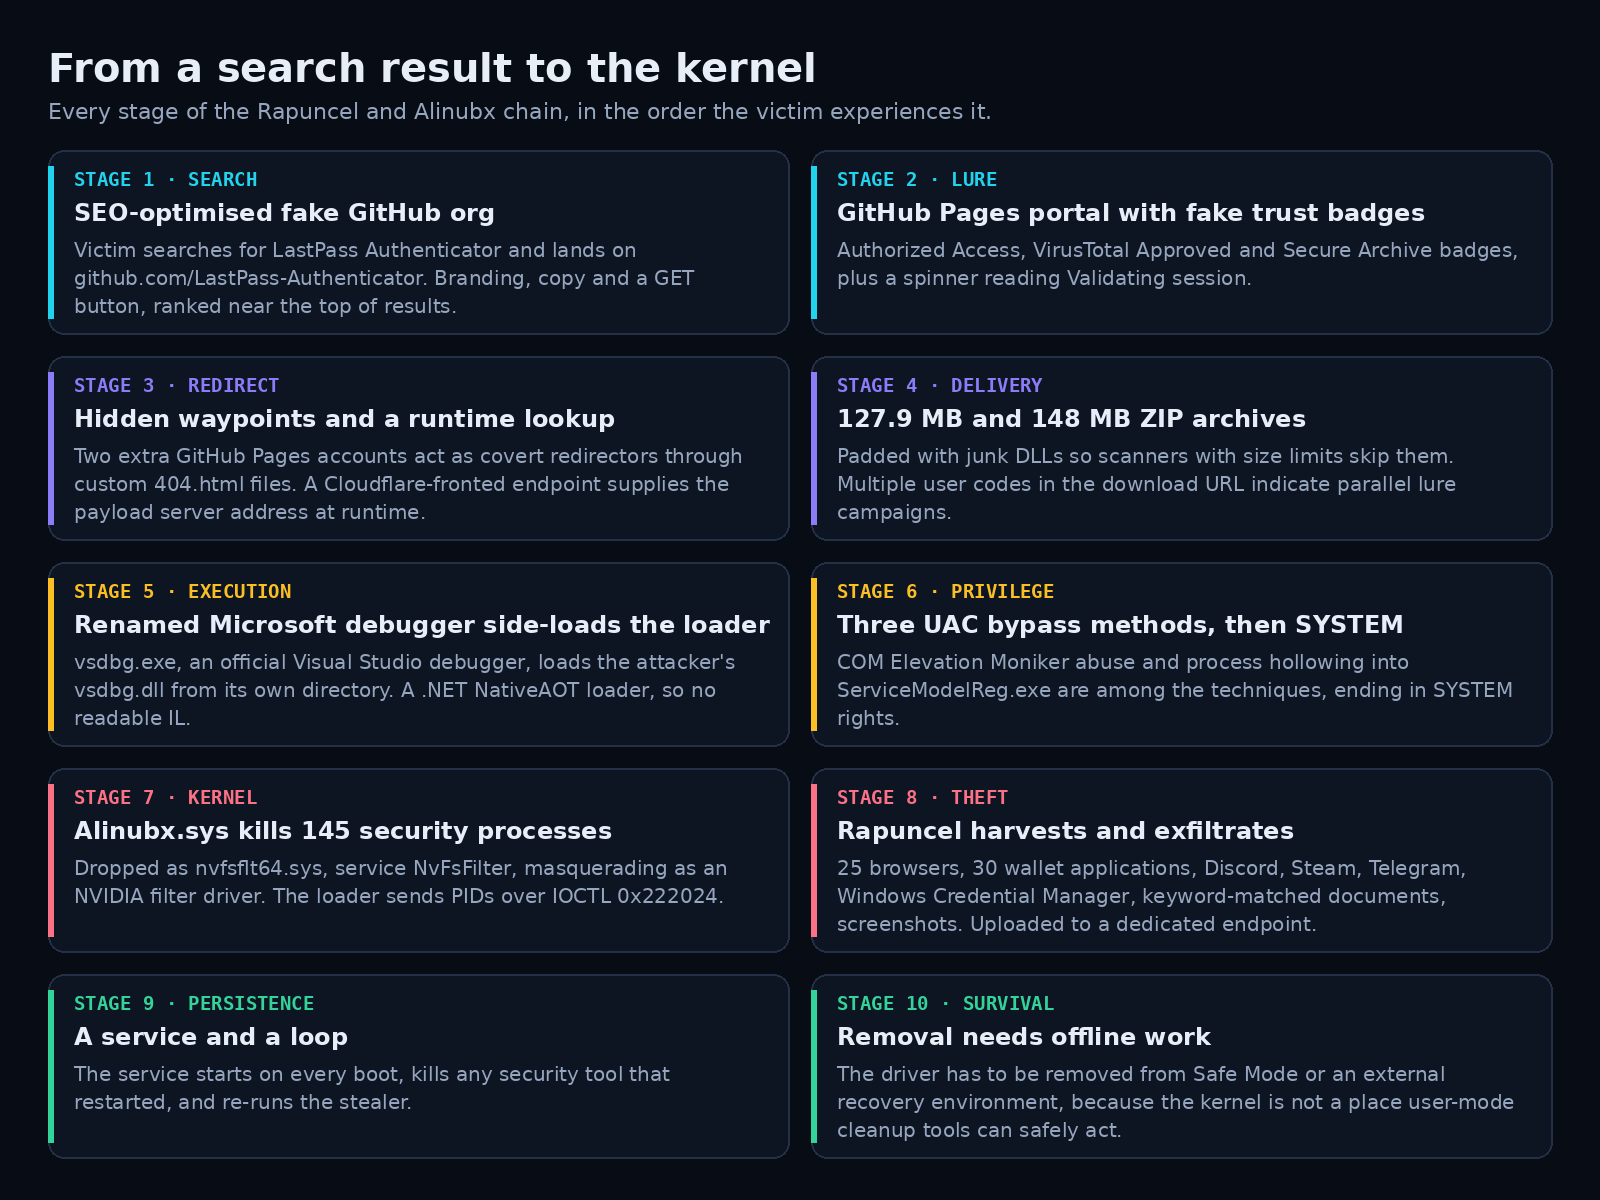
Inside the Rapuncel campaign: a fake installer, a renamed kernel driver, and 145 dead security processes
A fake LastPass Authenticator page on GitHub. A kernel driver signed by Microsoft’s own hardware programme. A stealer that kills 145 security processes, survives a reboot and keeps…
-
Threat digest: 2026-09-22
A cluster of compromised signing keys drained the Fetch.ai and NuNet bridges and minted hundreds of millions of tokens across the ASI Alliance ecosystem, CISA's deadline passed for…
-
Threat digest: 2026-09-21
A quiet weekend: Checkmarx detailed an npm supply chain campaign that hides its loader inside a btree library to slip past install-script blocks, researchers published two escapes from…
-
Threat digest: 2026-09-20
A six agency advisory attributed the WaterPlum job interview campaign to North Korea after at least 30,000 devices were infected and 10.71 million dollars in crypto was taken,…
-
Threat digest: 2026-09-19
CISA added three exploited Linux kernel flaws to its KEV catalog, Check Point and WordPress shipped critical fixes, Microsoft closed a maximum severity Azure AI Foundry bug, and…
-
Threat digest: 2026-09-18
A 23.6 million record breach at image host Gyazo, a critical remote code execution flaw in the Unbound DNS resolver, confirmed cyberattacks on two tankers bound for Texas,…