ARCHIVE
Tag: detection-engineering
-
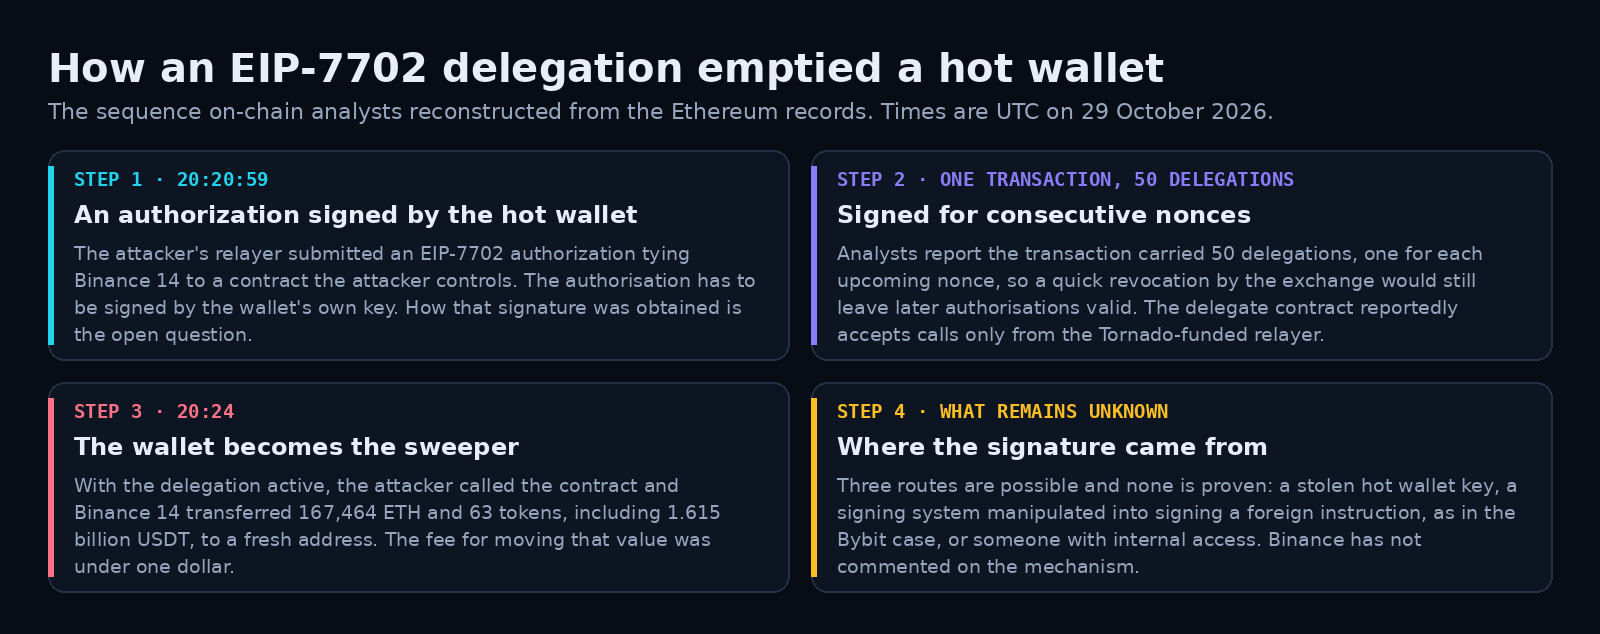
Security bulletin: Binance hot wallet compromise, 29 October 2026
Bulletin ISB-2026-10-30-01. Status: ongoing, under investigation. Severity: critical. Last updated 01:15 UTC on 30 October 2026. This bulletin covers a live incident; figures are moving and each is…
-
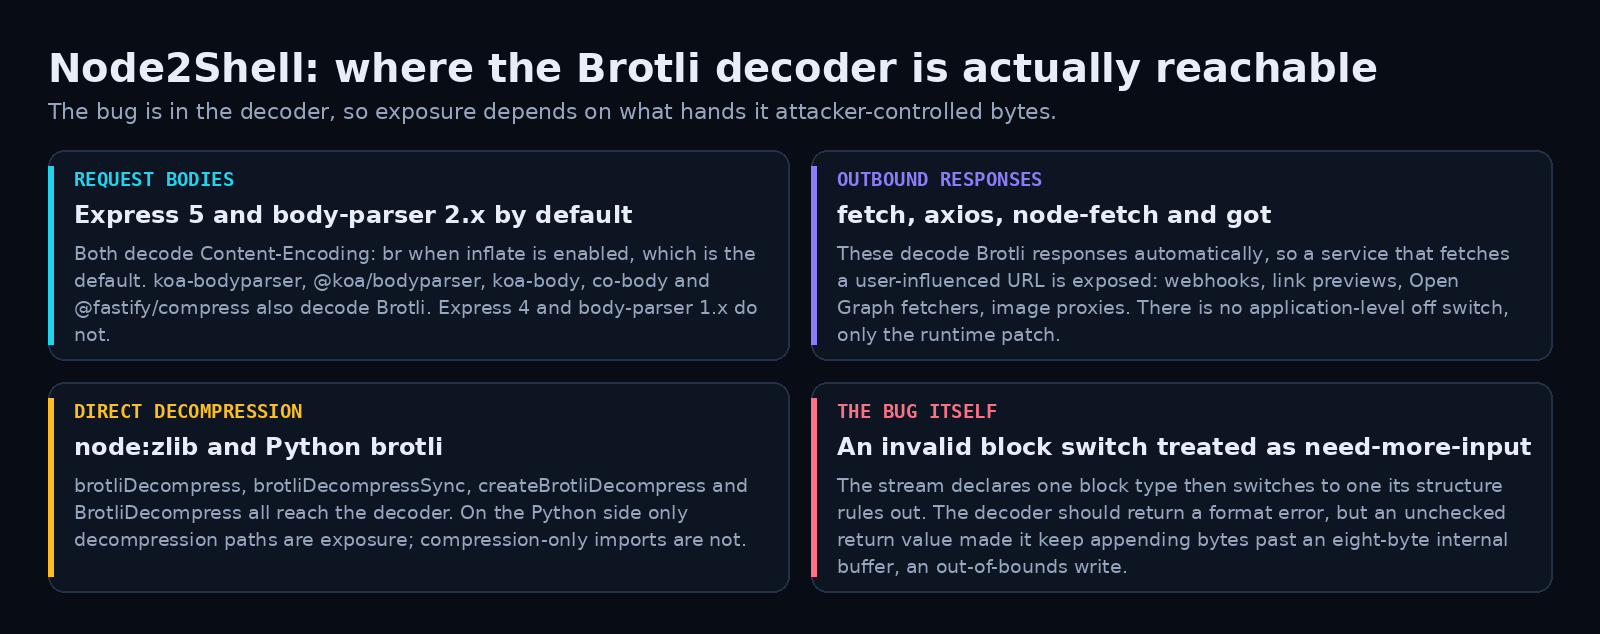
Node2Shell: the Brotli decoder bug behind CVE-2026-111497, where it is reachable, and how to detect it
Node2Shell is the nickname that Imperva and then the wider community attached to CVE-2026-111497, an out-of-bounds write in Google’s Brotli decoder that ships inside Node.js and a long…
-
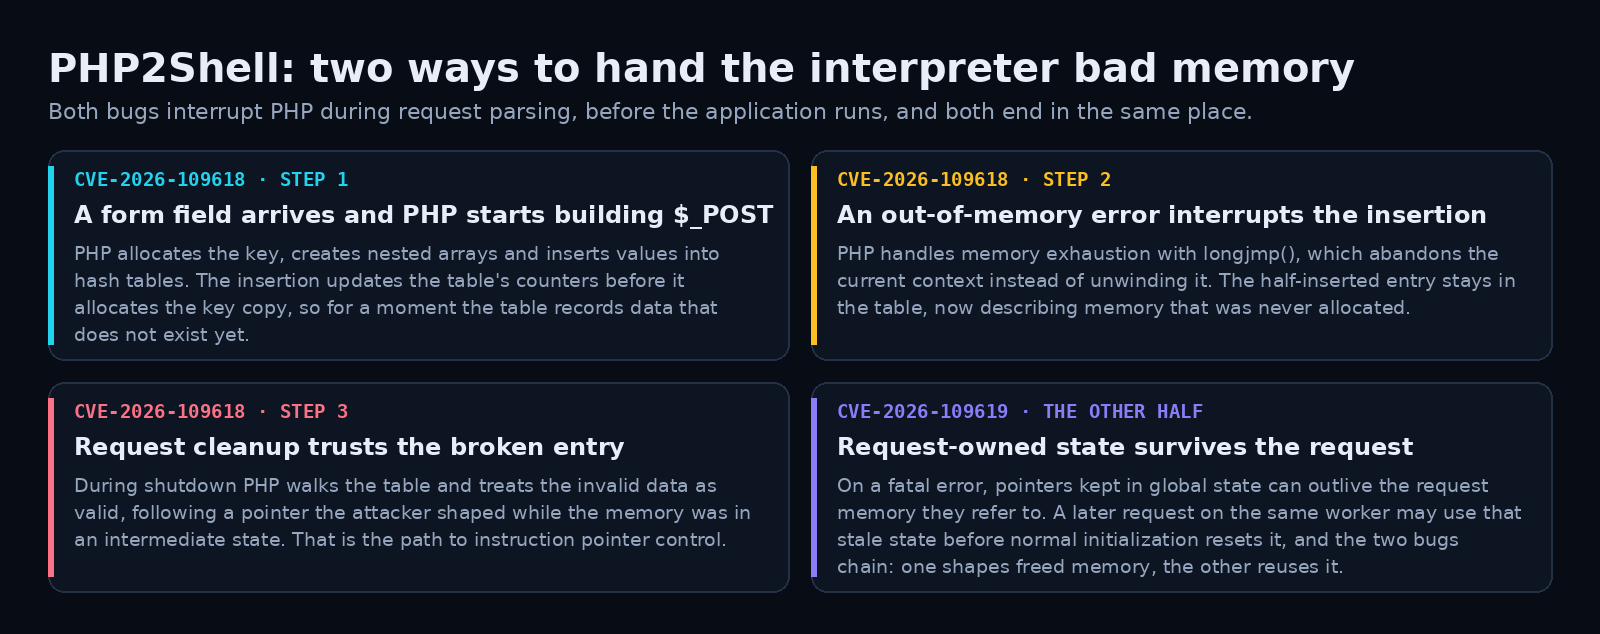
PHP2Shell: the two PHP bugs behind CVE-2026-109618 and CVE-2026-109619, and how to tell if you were hit
PHP2Shell is the name that stuck to two memory-safety vulnerabilities in PHP’s core request handling, CVE-2026-109618 and CVE-2026-109619, both rated 9.2 under CVSS v4 and both allowing unauthenticated…
-
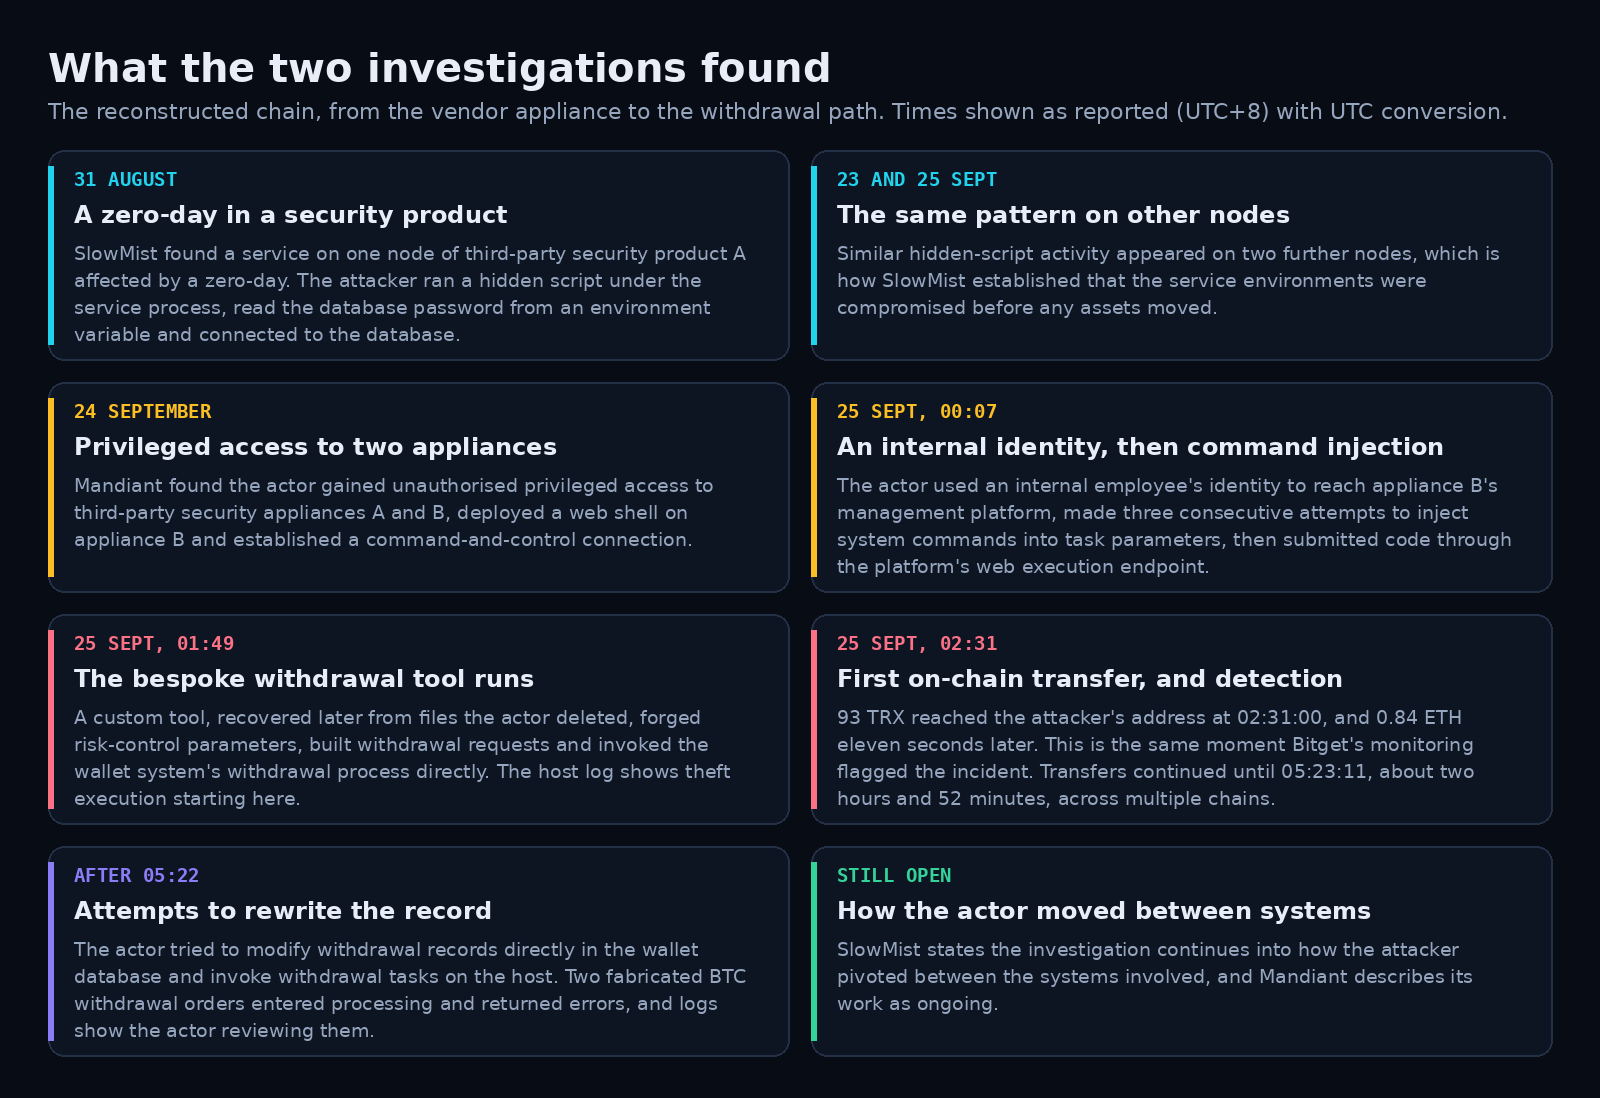
Bitget follow-up: what SlowMist and Mandiant found, and why the security appliances were the story
Two independent investigations into the Bitget theft have now been published, and between them they answer the question our analysis of 25 September had to leave open [7].…
-
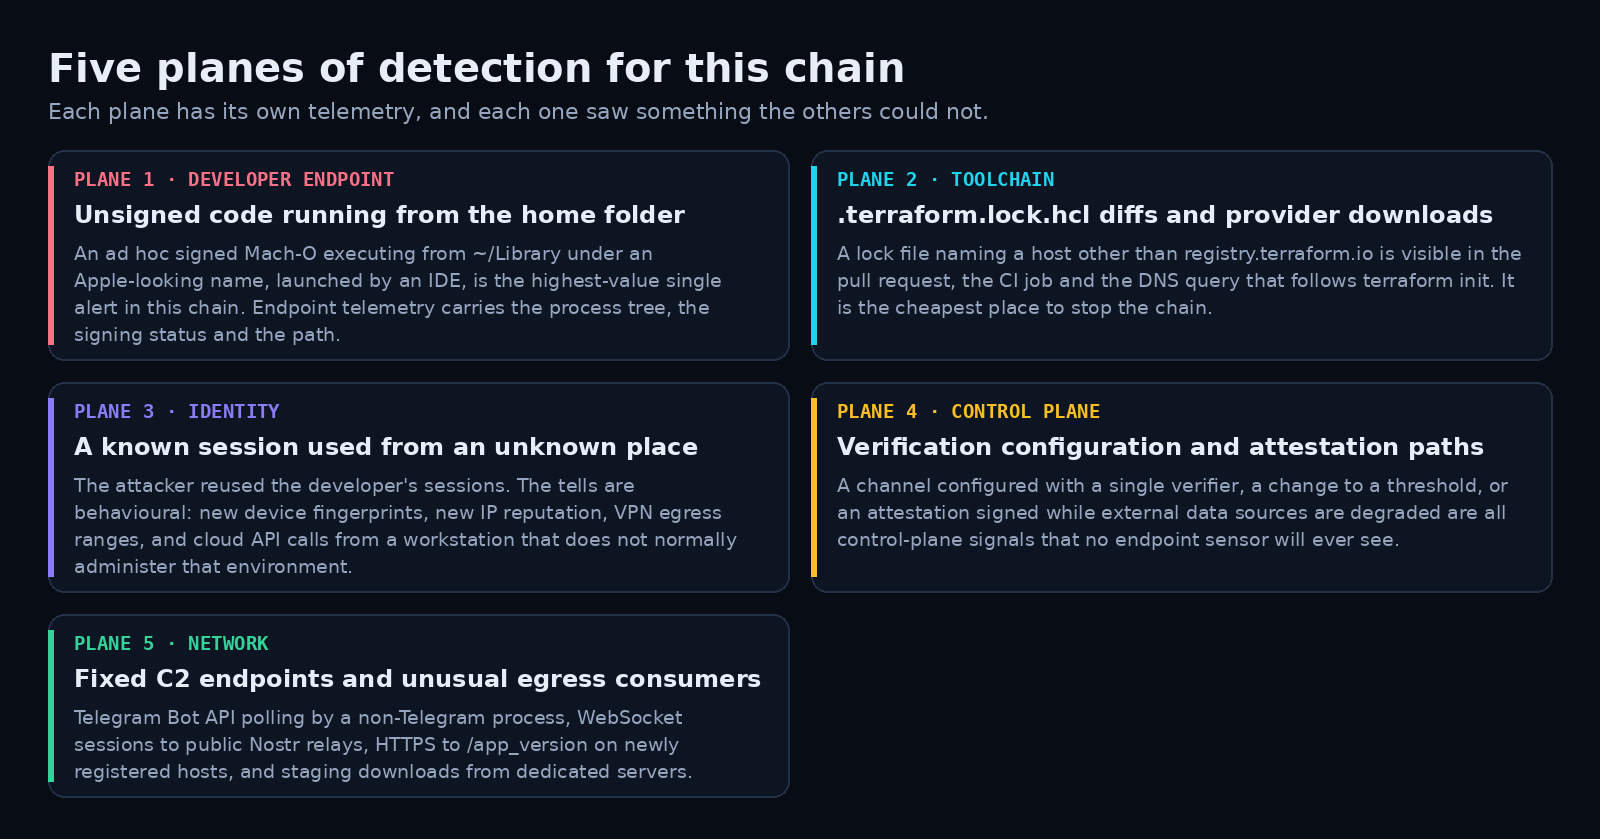
Detecting and stopping the DPRK developer chain: a control map for Terraform, macOS and cloud
The companion post to this one walks the TraderTraitor chain from a fake interview to a $292 million theft. This post is the working half: what to detect…
-
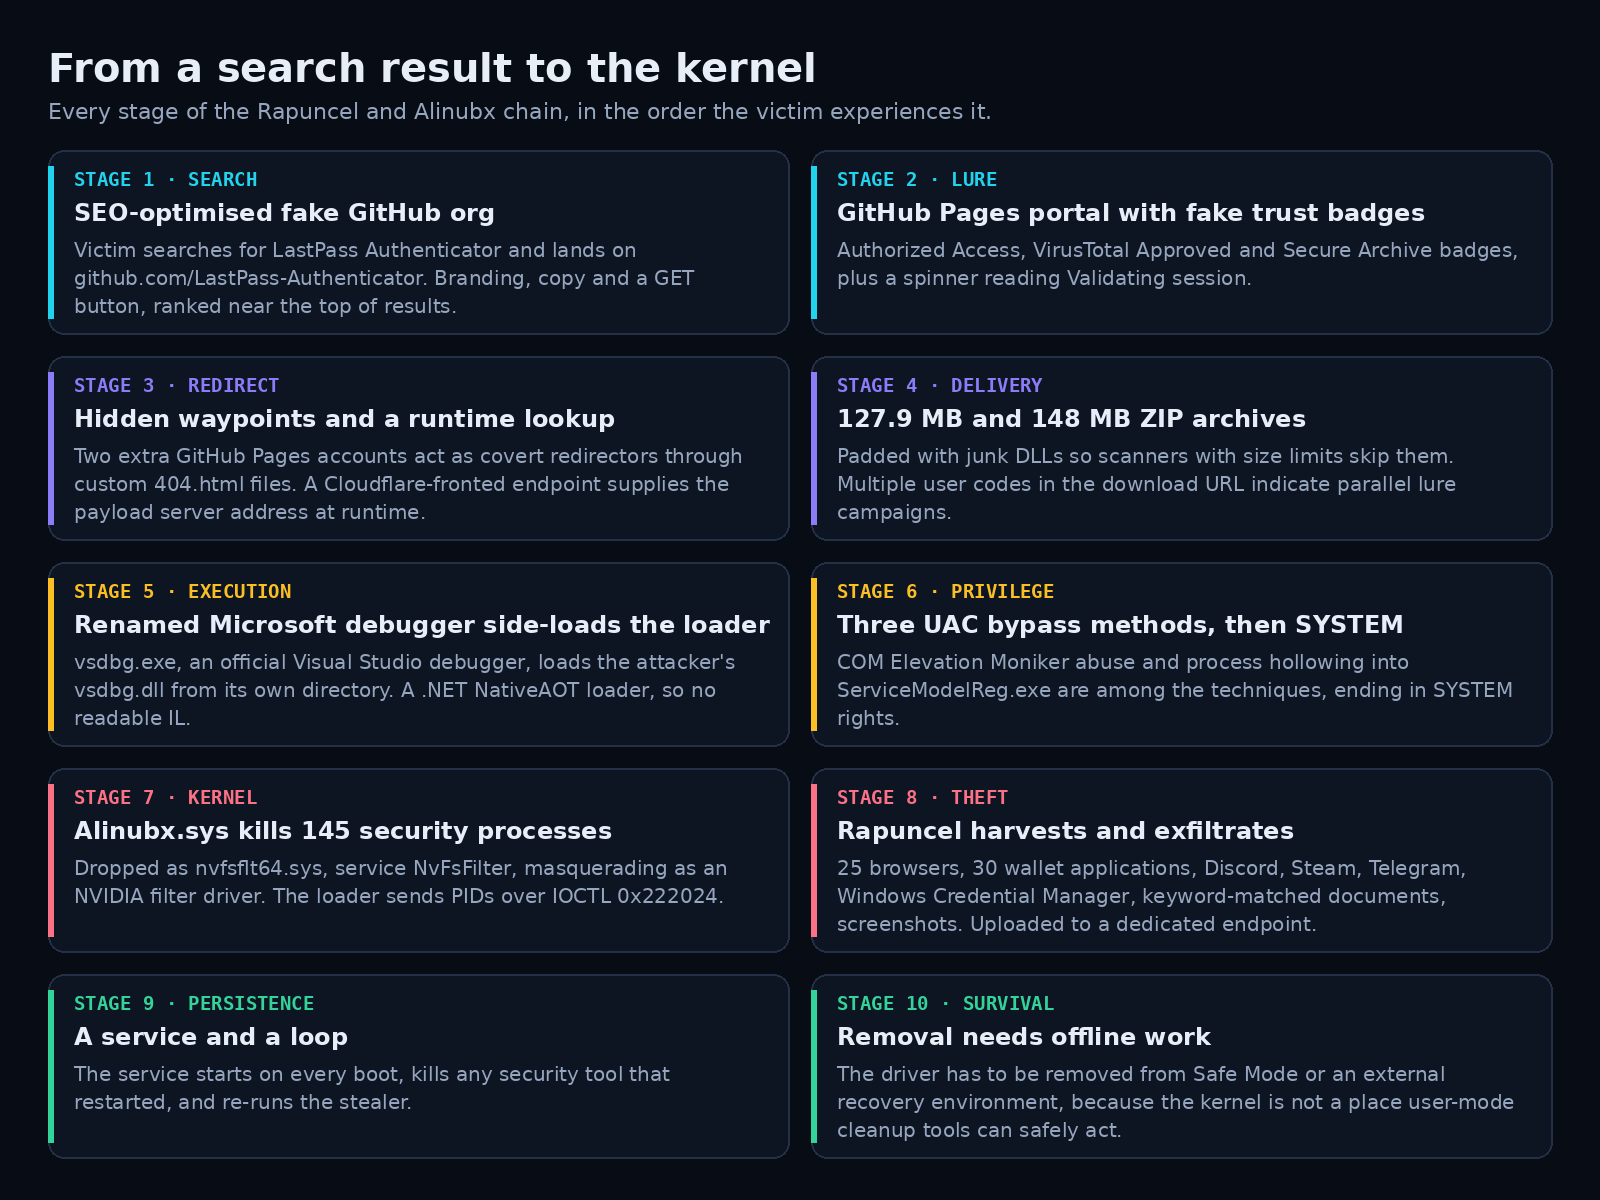
Inside the Rapuncel campaign: a fake installer, a renamed kernel driver, and 145 dead security processes
A fake LastPass Authenticator page on GitHub. A kernel driver signed by Microsoft’s own hardware programme. A stealer that kills 145 security processes, survives a reboot and keeps…
-
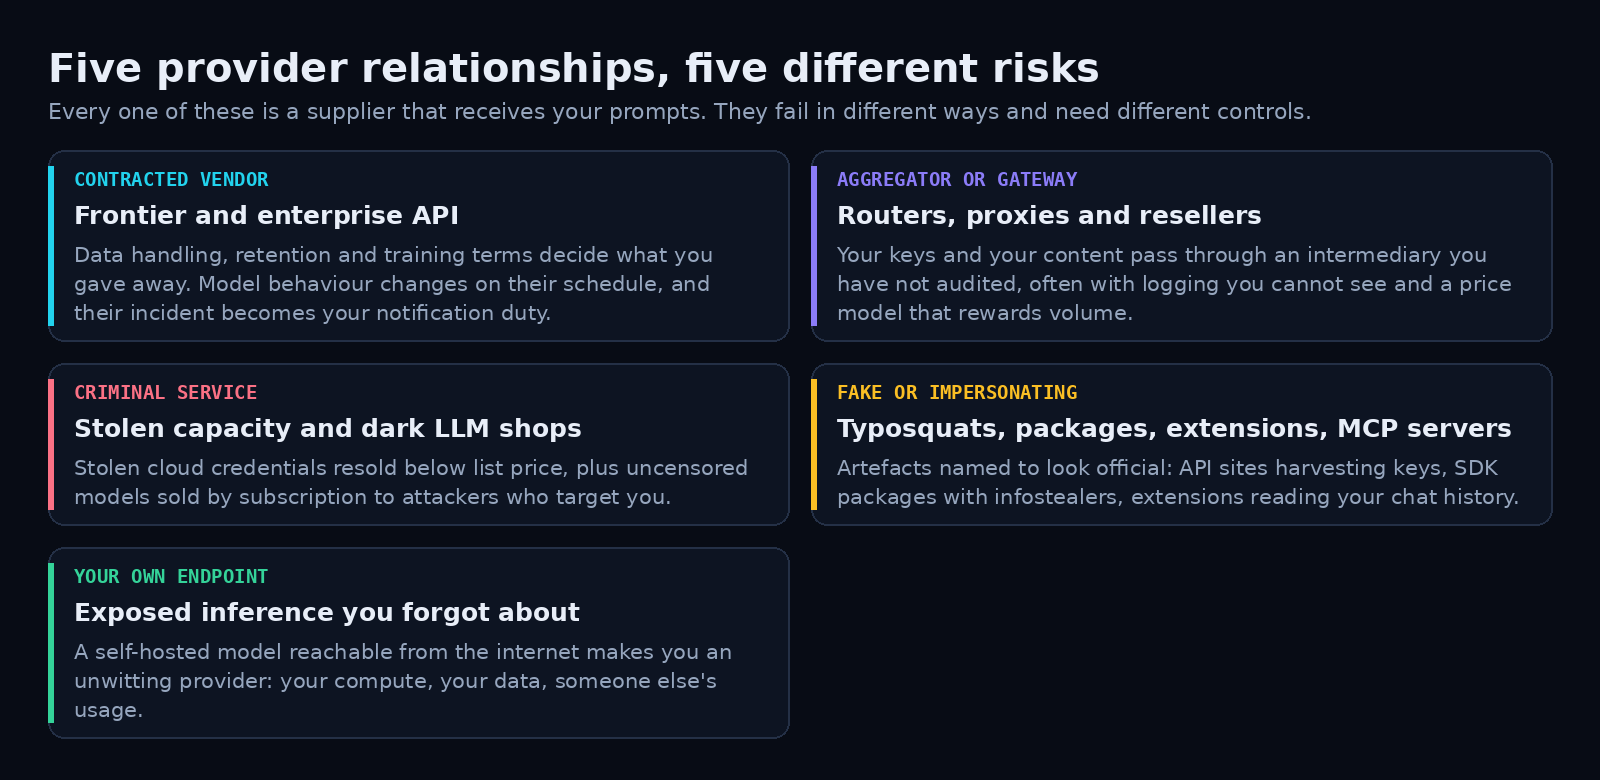
Malicious LLM providers and APIs: the third-party risk that is not on your architecture diagram
Your architecture diagram shows your cloud, your identity provider and your SIEM. It almost certainly does not show the six or seven places where prompts, documents and API…
-
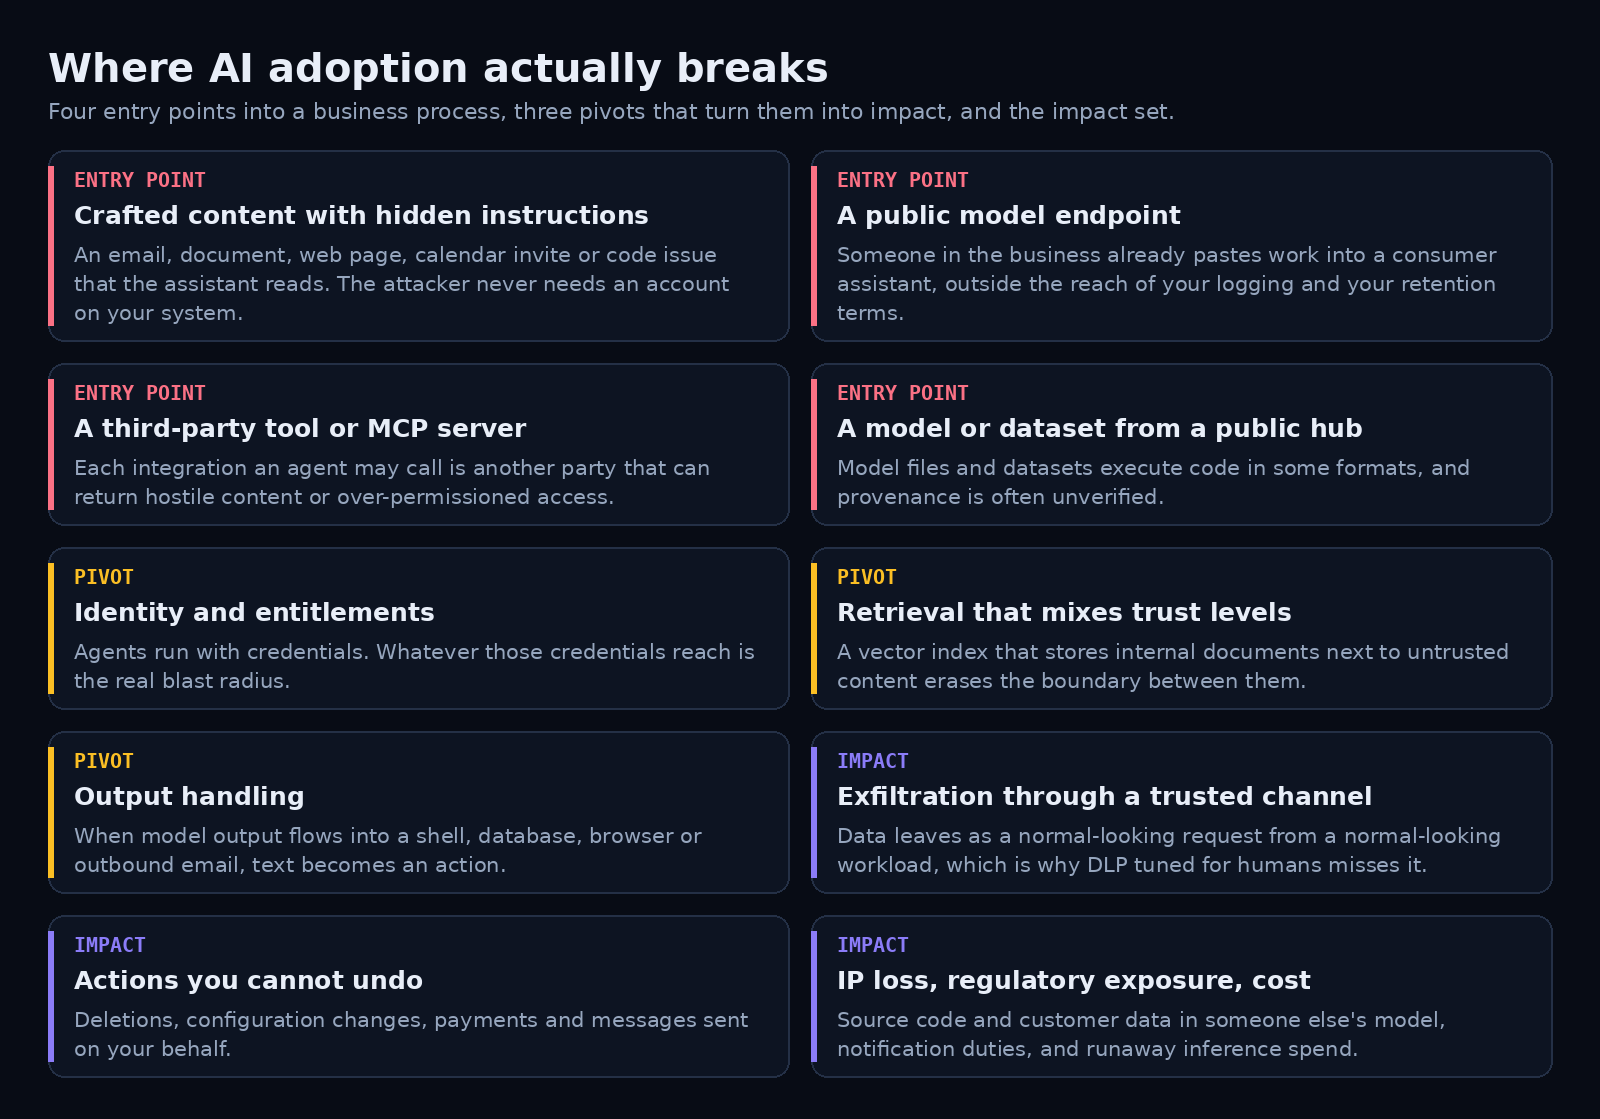
Adopting AI without losing control: the evidence on risk, and the controls that hold
Most companies are no longer deciding whether to adopt AI. They are deciding whether adoption happens inside a control framework or around one. The risk is not speculative:…
-
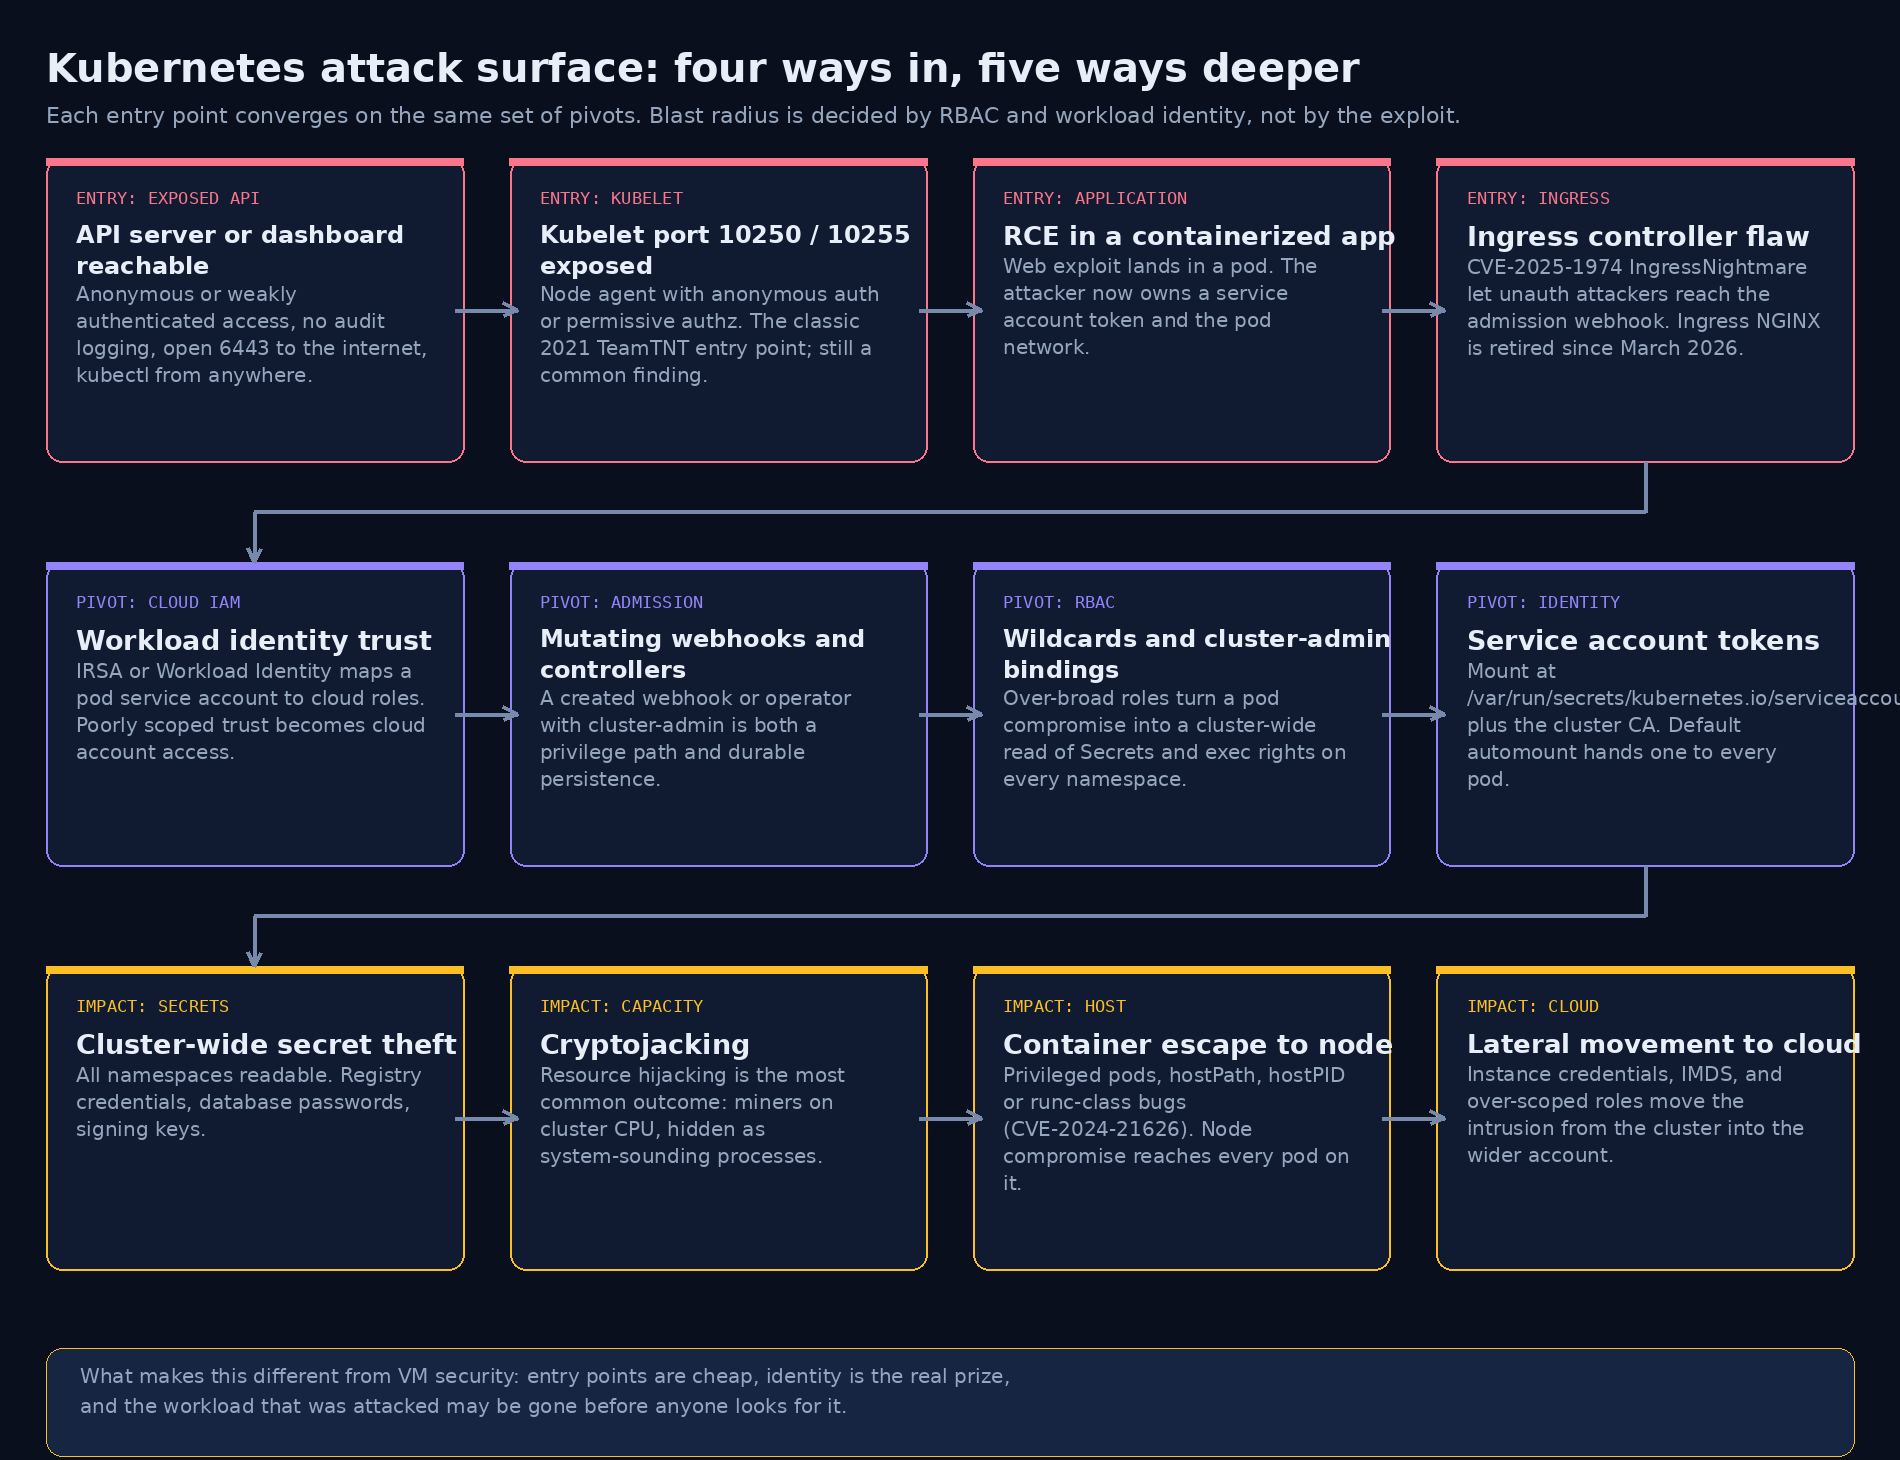
Why Kubernetes security is hard, and what to do about it: a deep dive beyond the interviews
Kubernetes is the operating system of modern cloud infrastructure, and it is genuinely harder to defend than the environments most security teams grew up on. Expel’s March 2026…