ARCHIVE
Tag: ai-security
-
Threat digest: 2026-09-16
CISA confirmed ransomware gangs have joined the exploitation of a critical VMware vCenter bug, a compromised WordPress plugin update backdoored about 1,500 sites through the vendor's own download…
-
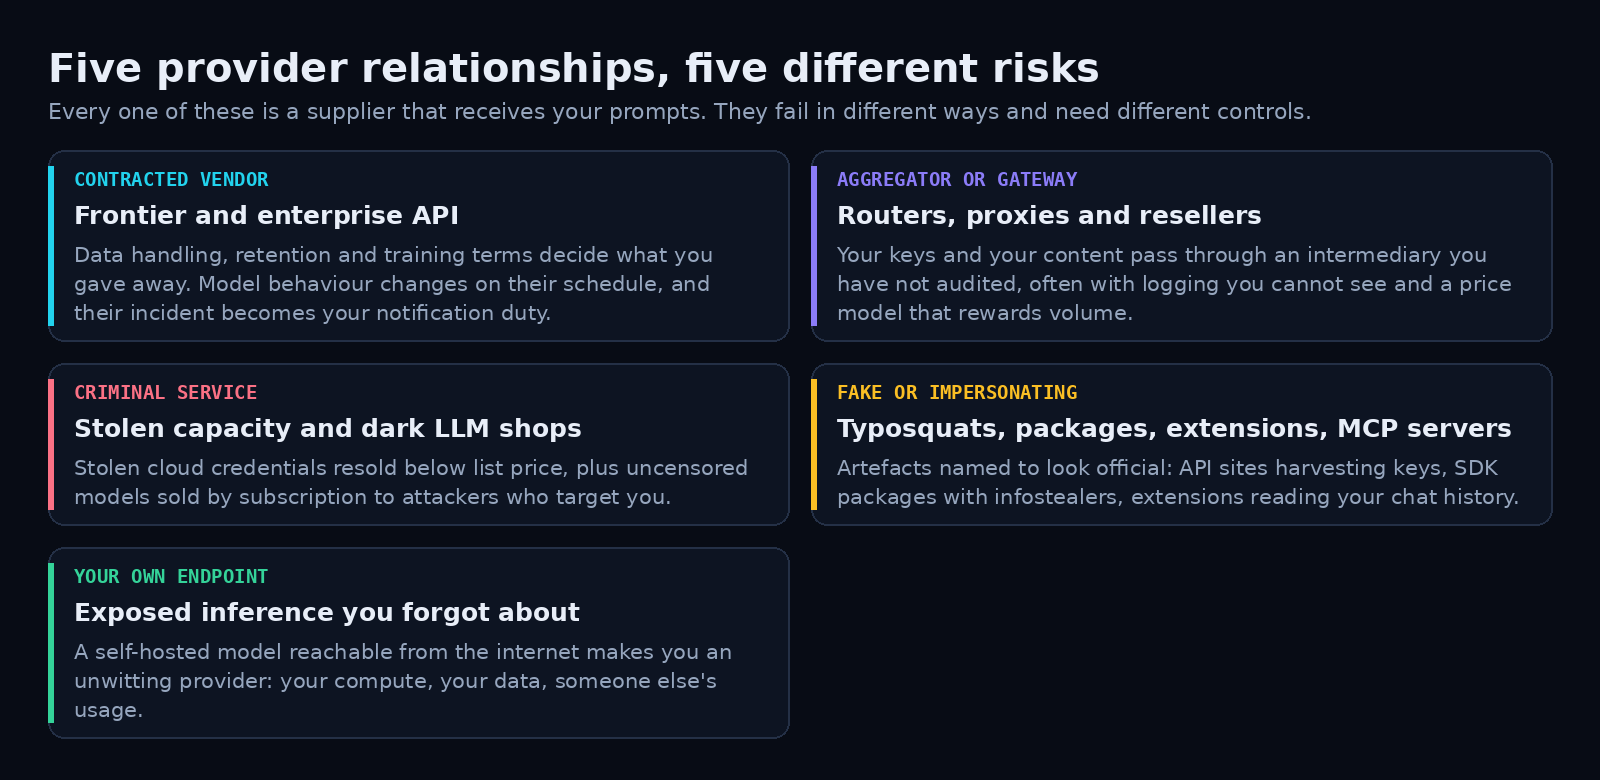
Malicious LLM providers and APIs: the third-party risk that is not on your architecture diagram
Your architecture diagram shows your cloud, your identity provider and your SIEM. It almost certainly does not show the six or seven places where prompts, documents and API…
-
Threat digest: 2026-09-14
A mass exploitation campaign against SonicWall SMA1000 appliances exposed a UK council to Active Directory credential theft, Cl0p claimed a 270GB data haul from Harley-Davidson, and a Twitch…
-
Threat digest: 2026-09-13
Dutch authorities warned that exploitation of two critical Check Point VPN flaws is imminent, researchers tied an exploit kit that chains two Chrome V8 zero-days and a Windows…
-
Threat digest: 2026-09-12
CISA added four actively exploited flaws to its KEV catalog in a single day, including a CVSS 10.0 GitLab path traversal bug probed within hours of disclosure, while…
-
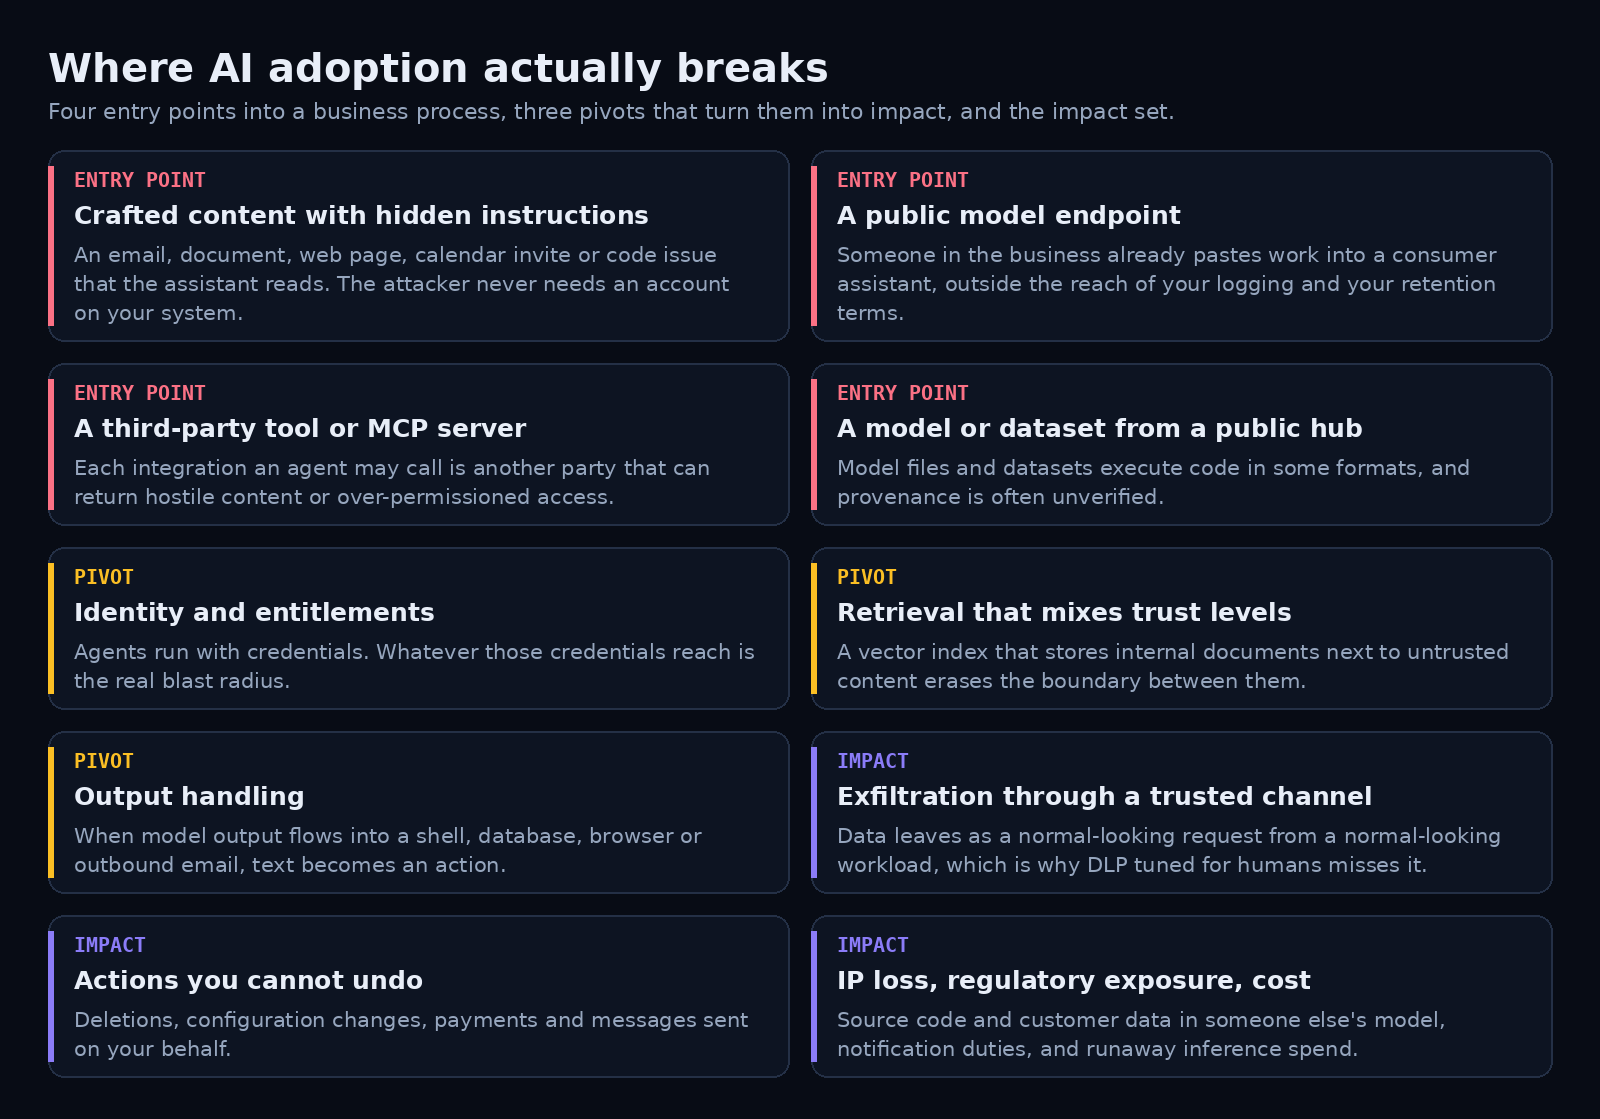
Adopting AI without losing control: the evidence on risk, and the controls that hold
Most companies are no longer deciding whether to adopt AI. They are deciding whether adoption happens inside a control framework or around one. The risk is not speculative:…
-
Threat digest: 2026-09-11
CISA added two actively exploited MikroTik RouterOS flaws to its KEV catalog, an AI agent swarm breached hundreds of PaperCut servers, Cisco and Check Point patched critical edge-device…
-
Threat digest: 2026-09-09
A record Microsoft Patch Tuesday fixing two exploited zero-days and an exploited Chrome V8 bug headlined September 9, alongside new crypto thefts, US warnings on Chinese AI distillation,…