ARCHIVE
Tag: supply-chain
-
Threat digest: 2026-10-31
A record $6.3bn theft from Binance, attributed to North Korea, dominates the day, alongside two exploited Ivanti VPN flaws, a CVSS 10.0 GitLab remote code execution flaw used…
-
Threat digest: 2026-10-28
Two CISA KEV additions, an exploited Adobe Commerce upload flaw and the Brotli memory bug, lead a day that also brought a ransomware threat against 26,739 Onamae cloud…
-
Threat digest: 2026-10-27
CISA adds PHP2Shell to its exploited catalog as honeypots record working shells, Microsoft and others rush emergency patches for the Node2Shell Brotli flaw, and a 525,000 person breach…
-
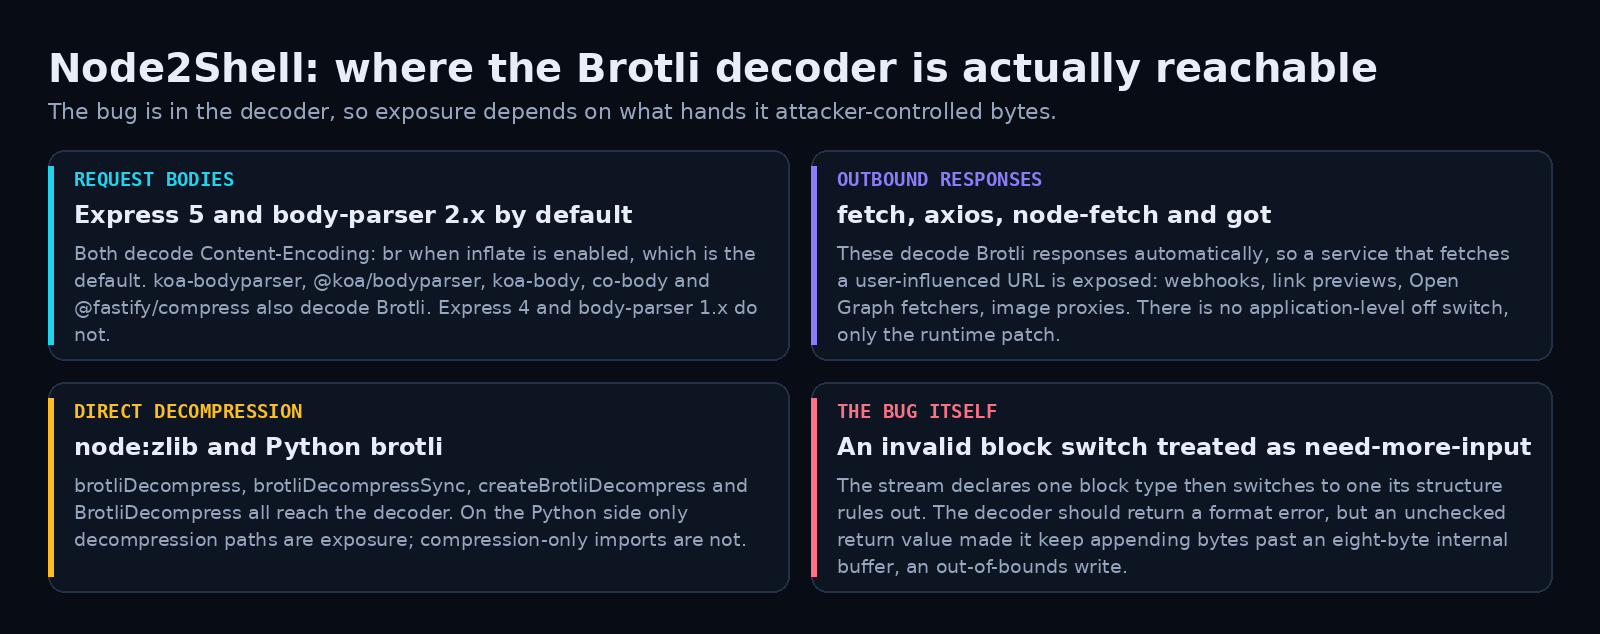
Node2Shell: the Brotli decoder bug behind CVE-2026-111497, where it is reachable, and how to detect it
Node2Shell is the nickname that Imperva and then the wider community attached to CVE-2026-111497, an out-of-bounds write in Google’s Brotli decoder that ships inside Node.js and a long…
-
Threat digest: 2026-10-26
An agentic attacker reached MFA secrets at a European government body within two hours, Tailscale SSH flaws went public with no patch, Microsoft shipped unscheduled .NET fixes, and…
-
Threat digest: 2026-10-25
PHP exploitation attempts keep climbing, a leaked LiteLLM master key turned into a poisoned package release, a ten week token replay campaign slipped past MFA at 79 organisations,…
-
Threat digest: 2026-10-24
PHP2Shell exploitation attempts escalated into Mirai botnet delivery while researchers published a working ASLR bypass, CISA added two more exploited flaws to its KEV catalog, and an AI…
-
Threat digest: 2026-10-23
PHP2Shell exploitation was traced back four days before its patches shipped, attackers exploited a third VeloCloud Orchestrator zero-day, and an Indian certificate authority began exiting the TLS business…
-
Threat digest: 2026-10-22
PHP shipped emergency fixes for two critical PHP2Shell RCE flaws as exploitation attempts began, GitLab patched a CVSS 10.0 unauthenticated RCE, and a compromised LiteLLM release pushed a…