BLOG
Notes from the field
Threat analysis, detection engineering and hands-on training notes from the practice.
-
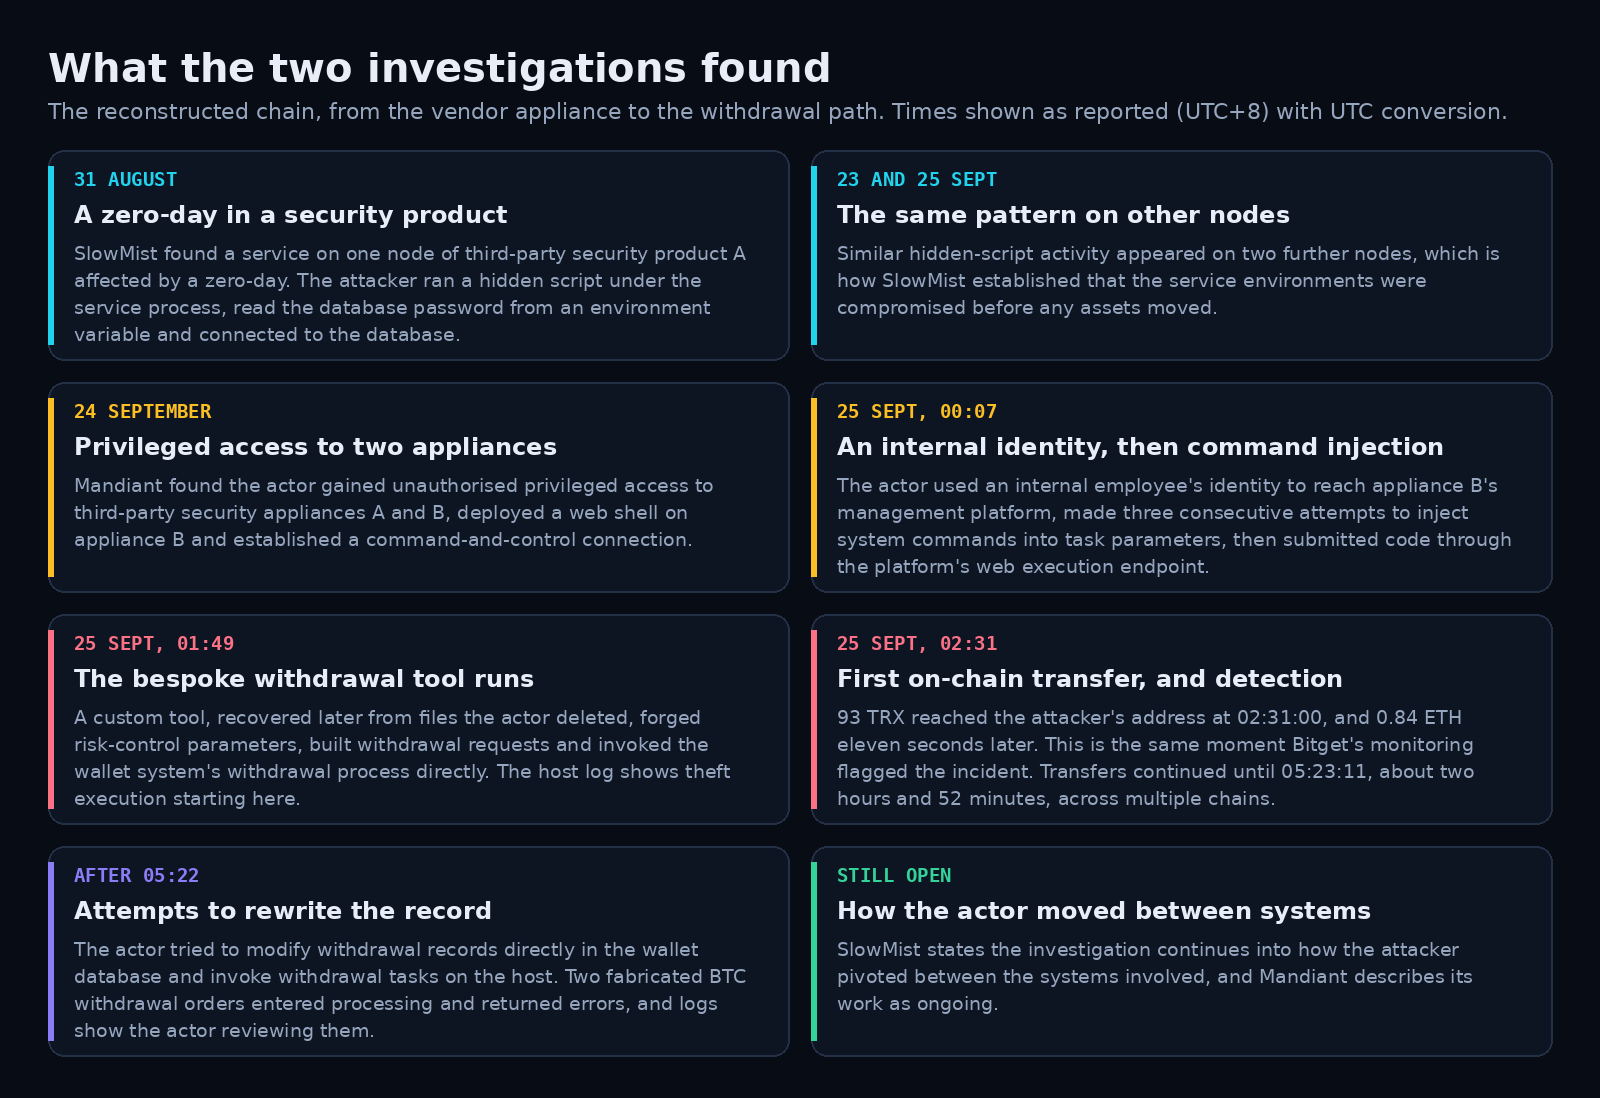
Bitget follow-up: what SlowMist and Mandiant found, and why the security appliances were the story
Two independent investigations into the Bitget theft have now been published, and between them they answer the question our analysis of 25 September had to leave open [7].…
-
Threat digest: 2026-09-30
CISA added Apple's exploited CoreGraphics flaw to its known exploited list while NetScaler zero-day attacks escalated into mass exploitation, a new Spectre v2 variant pulled Linux root password…
-
Threat digest: 2026-09-29
CISA ordered US federal agencies to patch the exploited Citrix NetScaler zero-days by Wednesday, a destructive agent-driven campaign deleted Azure resources, Bitget traced its $387 million theft to…
-
Threat digest: 2026-09-28
Citrix patched two NetScaler remote code execution zero-days that CISA says are being exploited in the wild, a cluster of critical flaws landed in Joomla, WordPress, Froxlor, hMailServer…
-
Threat digest: 2026-09-27
ShinyHunters resumed mass exploitation of the patched Oracle PeopleSoft bug by encoding the URL path around WAF rules, the Bitget attacker moved about $83 million of unfreezable XRP,…
-
Threat digest: 2026-09-26
CISA moved a critical WordPress core flaw plus exploited SharePoint and MikroTik bugs onto its known exploited list, Kiteworks told customers worldwide to take servers offline ahead of…
-
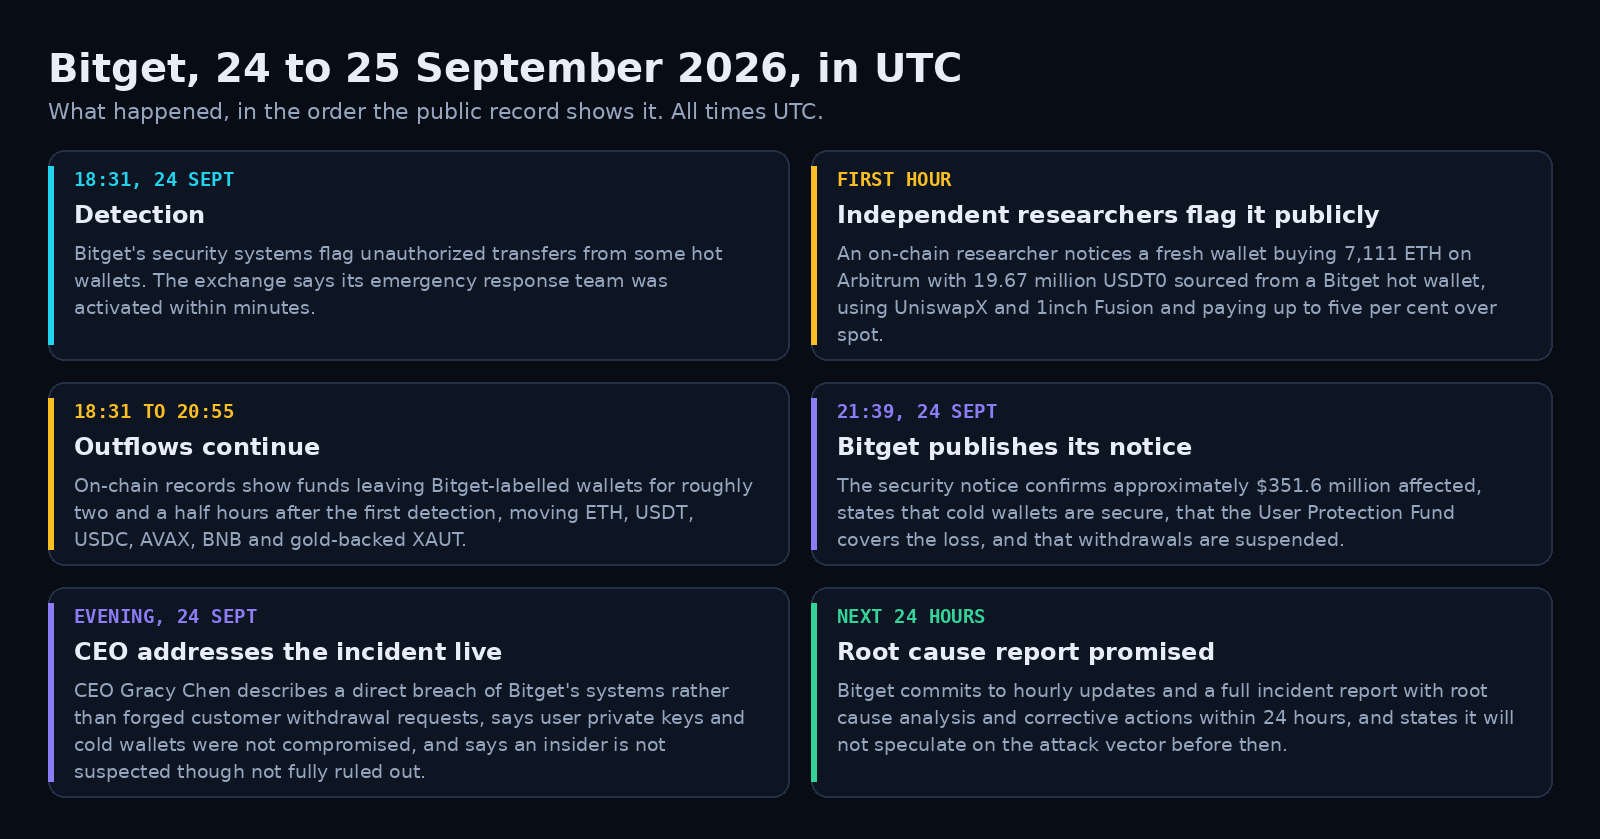
Bitget’s $351.6 million breach: the confirmed facts, the unproven claims, and what it means for exchange custody risk
At 18:31 UTC on 24 September 2026, Bitget’s security systems detected unauthorized transfers leaving some of its hot wallets. By the time the exchange published a notice three…
-
Threat digest: 2026-09-25
CISA added a maximum severity WSO2 authentication bypass and an Adobe Commerce flaw to its exploited list, a hot wallet drain at Bitget topped $351 million in the…
-
Threat digest: 2026-09-24
Actively exploited chains lead the day: unauthenticated takeover of internet-exposed MikroTik routers, a Chinese actor using Chrome and Windows zero-days, and a card skimming campaign run at scale…