ARCHIVE
Tag: supply-chain
-
Threat digest: 2026-10-12
AI-enabled attacks and supply chains led the day: ransomware crews exploited a Palo Alto GlobalProtect authentication bypass, a suspected North Korean crew backdoored a fake Terraform provider, lab…
-
Threat digest: 2026-10-10
SonicWall's maximum-severity SMA1000 flaw is now being exploited in the wild, Ledger is investigating a reported 87 million dollar drain from wallets bought through a reseller, and a…
-
Threat digest: 2026-10-09
CISA added five already-patched but actively exploited CVEs to its KEV catalog with a three-day fix deadline, FortiBleed operators began locking admins out of compromised Fortinet devices, and…
-
Threat digest: 2026-10-08
The FBI warned that the FortiBleed campaign has compromised more than 86,000 Fortinet devices and is still locking out admins, Atlassian's CVE-2026-21589 is being exploited within hours of…
-
Threat digest: 2026-10-07
Two WordPress flaws are being actively exploited to plant hidden administrator backdoors, alongside a critical Atlassian file-read flaw, a broad AI ad-portal phishing platform, and a run of…
-
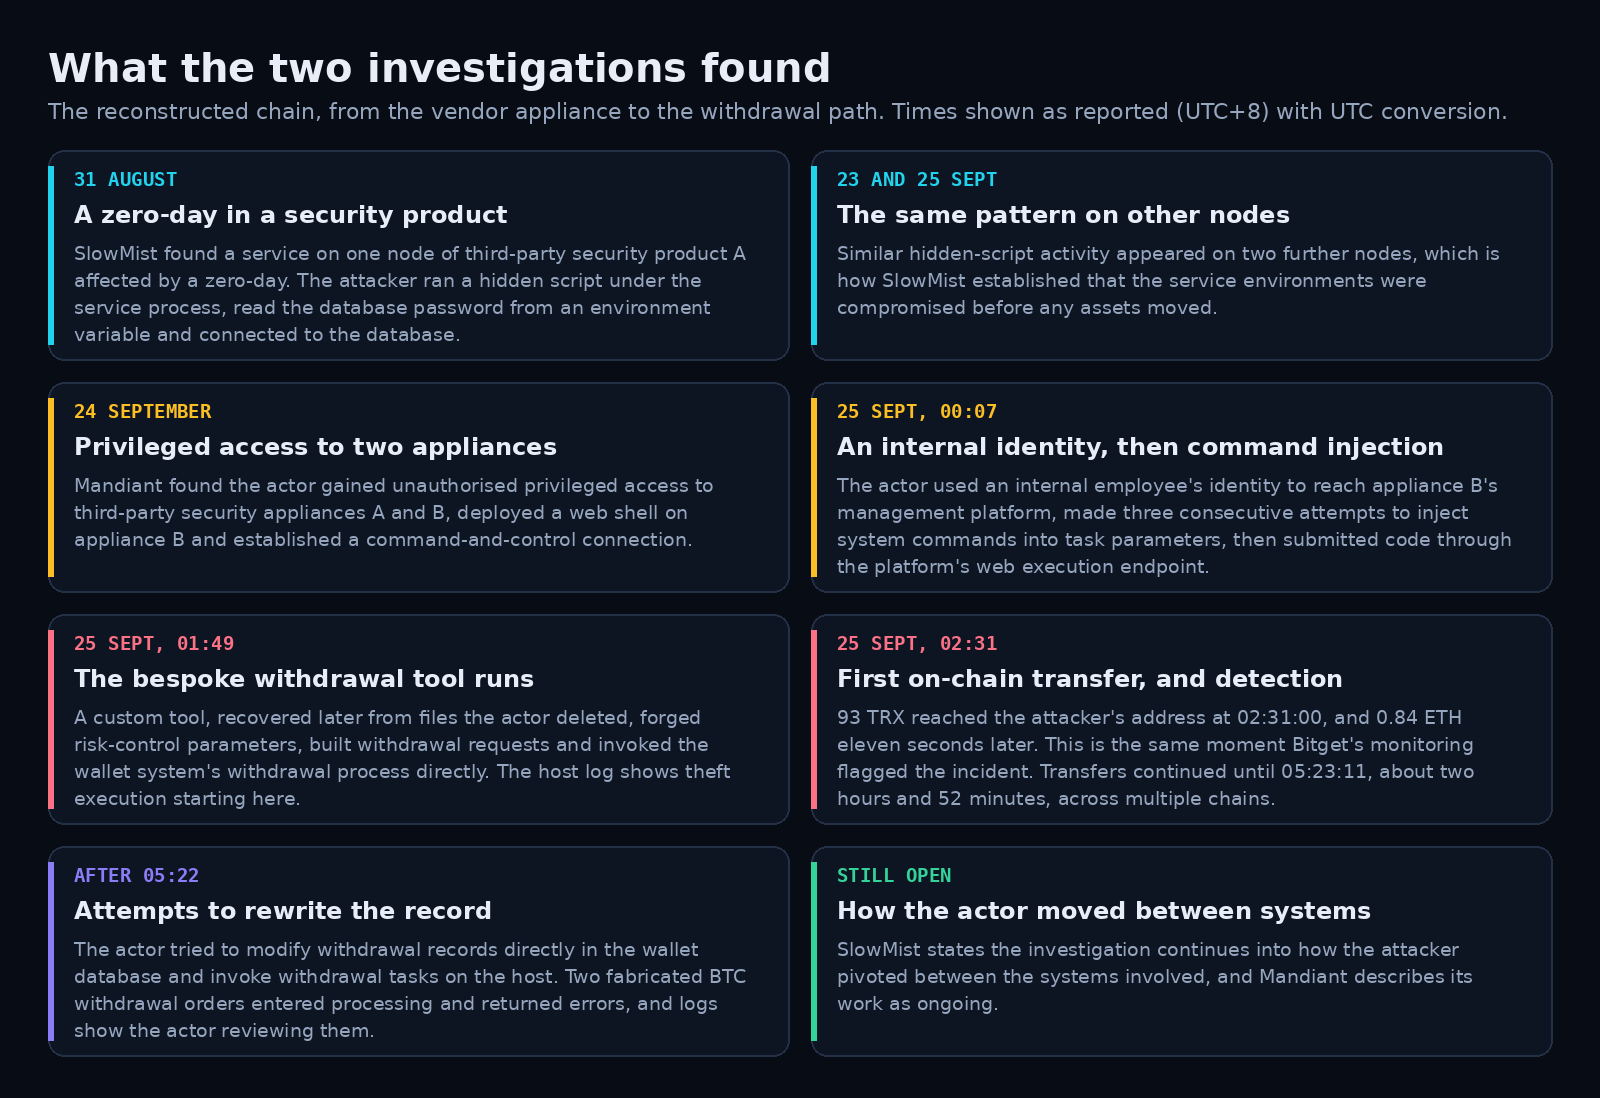
Bitget follow-up: what SlowMist and Mandiant found, and why the security appliances were the story
Two independent investigations into the Bitget theft have now been published, and between them they answer the question our analysis of 25 September had to leave open [7].…
-
Threat digest: 2026-09-30
CISA added Apple's exploited CoreGraphics flaw to its known exploited list while NetScaler zero-day attacks escalated into mass exploitation, a new Spectre v2 variant pulled Linux root password…
-
Threat digest: 2026-09-27
ShinyHunters resumed mass exploitation of the patched Oracle PeopleSoft bug by encoding the URL path around WAF rules, the Bitget attacker moved about $83 million of unfreezable XRP,…
-
Threat digest: 2026-09-26
CISA moved a critical WordPress core flaw plus exploited SharePoint and MikroTik bugs onto its known exploited list, Kiteworks told customers worldwide to take servers offline ahead of…